Repository navigation
docs(user): Tailscale HTTPS lists what the tailnet needs - #23759
WesleySmits wants to merge 1 commit into
Conversation


The Tailscale HTTPS section did not say that Serve needs MagicDNS and
HTTPS certificates on the tailnet, or that on Linux T3 Code needs
permission to manage Tailscale. Without them the server still starts but
can't add the HTTPS route, which is easy to miss.

Refs pingdotgg#16238

Co-Authored-By: Claude Opus 5.5 <noreply@anthropic.com>

Codex Review SummaryThis comment shows the latest Codex review activity on this pull request.
ℹ️ About Codex in GitHubYour team has set up Codex to review pull requests in this repo. Reviews are triggered when you
Codex reacts with 👀 while any review is running, comments if it has suggestions, and reacts with 👍 once all reviews finish with no findings. |
 github-actions
Bot
added
vouch:unvouched


ApprovabilityVerdict: Approved at Macroscope's review found this PR approvable — This PR only adds prerequisite guidance and links to the existing Tailscale HTTPS documentation. It changes no executable code, product defaults, schemas, or deployment behavior. You can add or adjust custom eligibility rules. Learn more. |

|
No actionable comments were generated in the recent review. 🎉 ℹ️ Recent review info
📝 Walkthrough
Merge Risk: ⚪ Minimal · up to
|


| Check name | Status | Explanation |
|---|---|---|
| Title check |  |
The title is concise, specific, and accurately describes the documentation change to the Tailscale HTTPS prerequisites. |
| Description check | |
The description covers the problem, documentation change, scope, issue reference, verification steps, observed results, and limitations. It clearly states that the change is documentation-only and ide… |
| Linked Issues check | |
Check skipped because no linked issues were found for this pull request. |
| Out of Scope Changes check | |
Check skipped because no linked issues were found for this pull request. |
Full details: Description check
-
Explanation
The description covers the problem, documentation change, scope, issue reference, verification steps, observed results, and limitations. It clearly states that the change is documentation-only and identifies the checks that were not performed.
✨ Finishing Touches
-
🧪 Generate unit tests (beta)
-
- Create a new PR
-
- Autofix · Keep fixing CodeRabbit findings and required CI, and resolving merge conflicts
Comment @coderabbitai help to get the list of available commands.


|
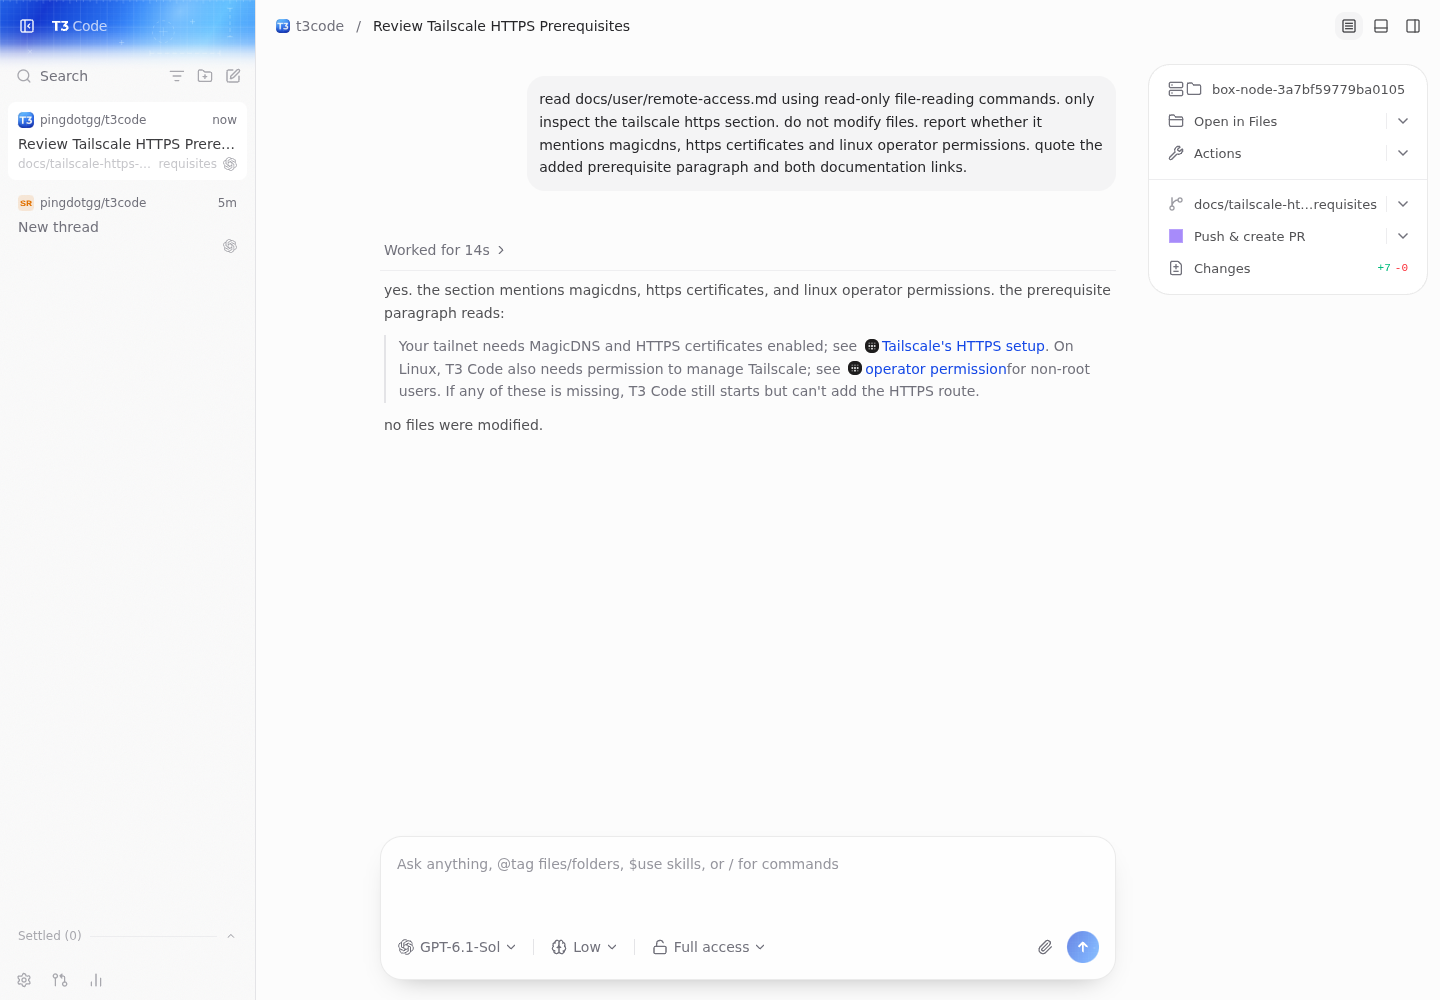
Note Written by Verified in a real dev environmentverified the documentation change at
Not verifiedthis vm has neither a tailscale installation nor an authenticated tailnet. i could not reproduce missing magicdns, disabled https certificates, or missing linux operator permission individually, nor successful https publication, prerequisite recovery, or cross-device access. the missing-executable case above is separate and does not prove those three cases. those claims remain supported by the linked upstream docs and source inspection, not a live tailnet run. native desktop, ios/android, macos/windows behavior was not exercised. no product ui changed. this pass verifies the documentation and local fallback/provider path, not end-to-end tailscale https. |


Problem
The Tailscale HTTPS section in
docs/user/remote-access.mdsays how to turn the route on, but not what the tailnet needs for it to work. Without MagicDNS and HTTPS certificates, or on Linux without permission to manage Tailscale, T3 Code still starts but no HTTPS route appears. Nothing in the guide points users to the cause (see #16238).Change
Six lines in
### Tailscale HTTPS, before the CLI examples:Both links go to Tailscale's own docs, so the setup steps and the public-ledger note stay there.
Scope and approval
Docs only, one problem: the existing workflow is hard to get working because its prerequisites aren't documented (CONTRIBUTING, existing workflow hard to find or understand). It doesn't change runtime behavior.
Refs #16238. Related: #23605 makes the server retry Serve after a failed start. That PR touches no docs, and these prerequisites still apply after it lands, since a retry can't succeed while one of them is missing. For the same reason this text gives no recovery or retry advice.
Verification
t3 pair --tailscalefails explicitly when there is no MagicDNS name or Serve/HTTPS is not enabled (apps/server/src/cli/pair.ts), and the server logs a warning and keeps running whentailscale servefails (apps/server/src/server.ts). The maintainer repro in [Bug]: Tailscale Serve failures are only logged as a warning; the server silently stays loopback-only #16238 shows the non-operator case:permission-denied, server ready,serve status{}.vp run check:changed: format pass; knip skipped (no code changed).git diff --checkis clean.🤖 Written by Claude Opus 5.5 via Claude Code in T3 Code.